Notification
Go to Home All Tools Compare Glossary Blog Contact

DNS Propagation Checker

Check DNS propagation across multiple public resolvers. Compare A, AAAA, CNAME, MX, TXT, NS, CAA, and SOA records and verify expected DNS values.

Resolver Comparison & Propagation Test

DNS Propagation Checker

Query multiple public DNS resolvers worldwide to verify DNS changes. Compare A, AAAA, CNAME, MX, TXT, NS, CAA, and SOA records and check propagation status based on sampled resolvers.

Query Configuration

If empty, resolvers are compared against the majority observed value.

Sampled Public Resolvers
  • • Cloudflare (1.1.1.1)
  • • Google DNS (8.8.8.8)
  • • Quad9 (9.9.9.9)
  • • Cisco OpenDNS
  • • Native System Resolver
Zero Data Retention

Queried domain names are processed in-memory solely to retrieve DNS records and return comparison metrics. Queries are never permanently stored, logged, or sent to third-party tracking scripts.

Propagation Status
Ready
Last Checked
--:--:--
Sampled Resolvers
0
Matching
0
Differing
0
No Answer / Error
0
Resolver Returned Value(s) TTL Status
Enter a domain and click Check Propagation to query public resolvers.

Understanding Resolver Differences & CDN Routing

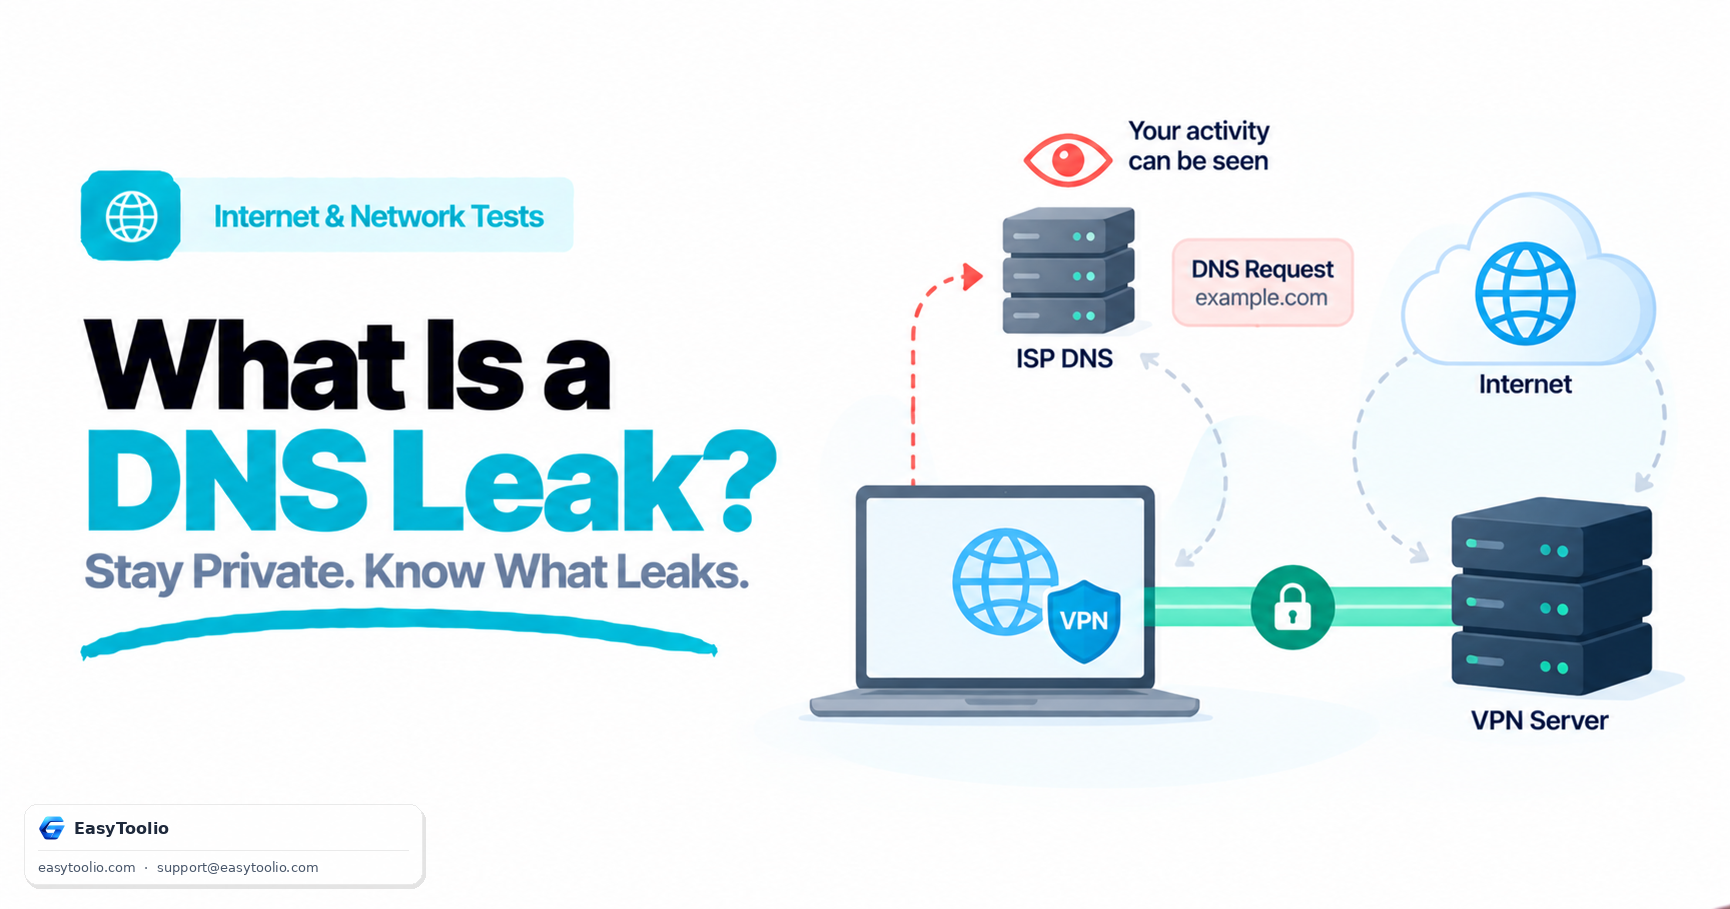
Different public DNS resolvers may legitimately return distinct IP addresses for modern websites. This occurs because major web services utilize:

  • Content Delivery Networks (CDNs) edge nodes
  • Anycast & GeoDNS proximity routing
  • Round-Robin Load Balancing pools
  • TTL Cache Countdown window offsets

Differing IP addresses do not automatically mean DNS is not propagated. Always compare expected values against your authoritative nameserver configuration.

Education

Complete Guide to Global DNS Propagation & Name Server Caching

01

What is DNS Propagation?

DNS propagation is the timeframe required for domain name record changes (A, AAAA, CNAME, MX, TXT, NS) to update across public resolvers and ISP caching servers globally after changing authoritative nameserver entries.
02

Why DNS Records Take 24 to 48 Hours to Propagate

When you modify a DNS record, recursive resolvers store the previous value in local cache for the duration specified by the record Time To Live (TTL). Until the TTL expires on each individual resolver worldwide, queries will continue returning cached IP addresses.

03

Anycast DNS & GeoDNS Proximity Routing

Modern CDNs (Cloudflare, AWS CloudFront, Fastly) and Anycast networks return different IP addresses based on the geographic region of the querying resolver. Differing IP responses across global nodes often reflect optimal regional routing rather than incomplete propagation.

04

How to Speed Up DNS Record Updates

Before migrating servers or changing IP addresses, lower your record TTL value (e.g. from 86400 seconds to 300 seconds) 24 hours in advance. This ensures resolvers clear their cache quickly when the IP change is committed.

05

Flushing Local Computer & Browser DNS Caches

Your local operating system caches resolved IP addresses. On Windows, run "ipconfig /flushdns" in Command Prompt. On macOS, execute "sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder" in Terminal to clear local DNS resolution buffers.

06

Explore Related Network Diagnostic Utilities

Perform authoritative DNS queries with our <a href="/dns-lookup" class="text-cyan-400 hover:underline font-semibold">DNS Lookup Tool</a>, inspect domain WHOIS registration via the <a href="/domain-whois-checker" class="text-cyan-400 hover:underline font-semibold">WHOIS Checker</a>, test SSL certificates using the <a href="/ssl-certificate-checker" class="text-cyan-400 hover:underline font-semibold">SSL Certificate Checker</a>, and measure latency with the <a href="/ping-test" class="text-cyan-400 hover:underline font-semibold">Ping Test</a>.

Good to know

Questions, answered

Quick answers about how this tool works.

Most DNS updates take between 10 minutes and a few hours. However, depending on ISP caching policies and TTL settings, complete worldwide propagation can take up to 24-48 hours.

This happens either because some resolvers still have the old IP cached in TTL memory, or because the website uses Anycast / CDN routing to serve different regional edge IPs.

TTL is a numerical value (in seconds) set by domain administrators that instructs public resolvers how long they may cache a DNS record before re-querying the authoritative nameserver.

You cannot force third-party ISP resolvers to flush their cache. However, you can request manual cache flushes on public resolvers such as Google Public DNS (8.8.8.8) and Cloudflare (1.1.1.1) via their official web purge portals.

What do you need to work out next?

Search 244+ free tools by name, or pick a category below. Every one runs instantly in your browser — no signup, nothing to install.